Rate limits for private vulnerability reports
GitHub introduces daily per-user rate limits for private vulnerability reports to reduce automated spam. Maintainers can now set custom daily caps and maintain allow lists for trusted researchers. This operational change applies to public repositories with private reporting enabled across all GitHub plans, aiming to protect signal from noise without blocking legitimate security disclosures.
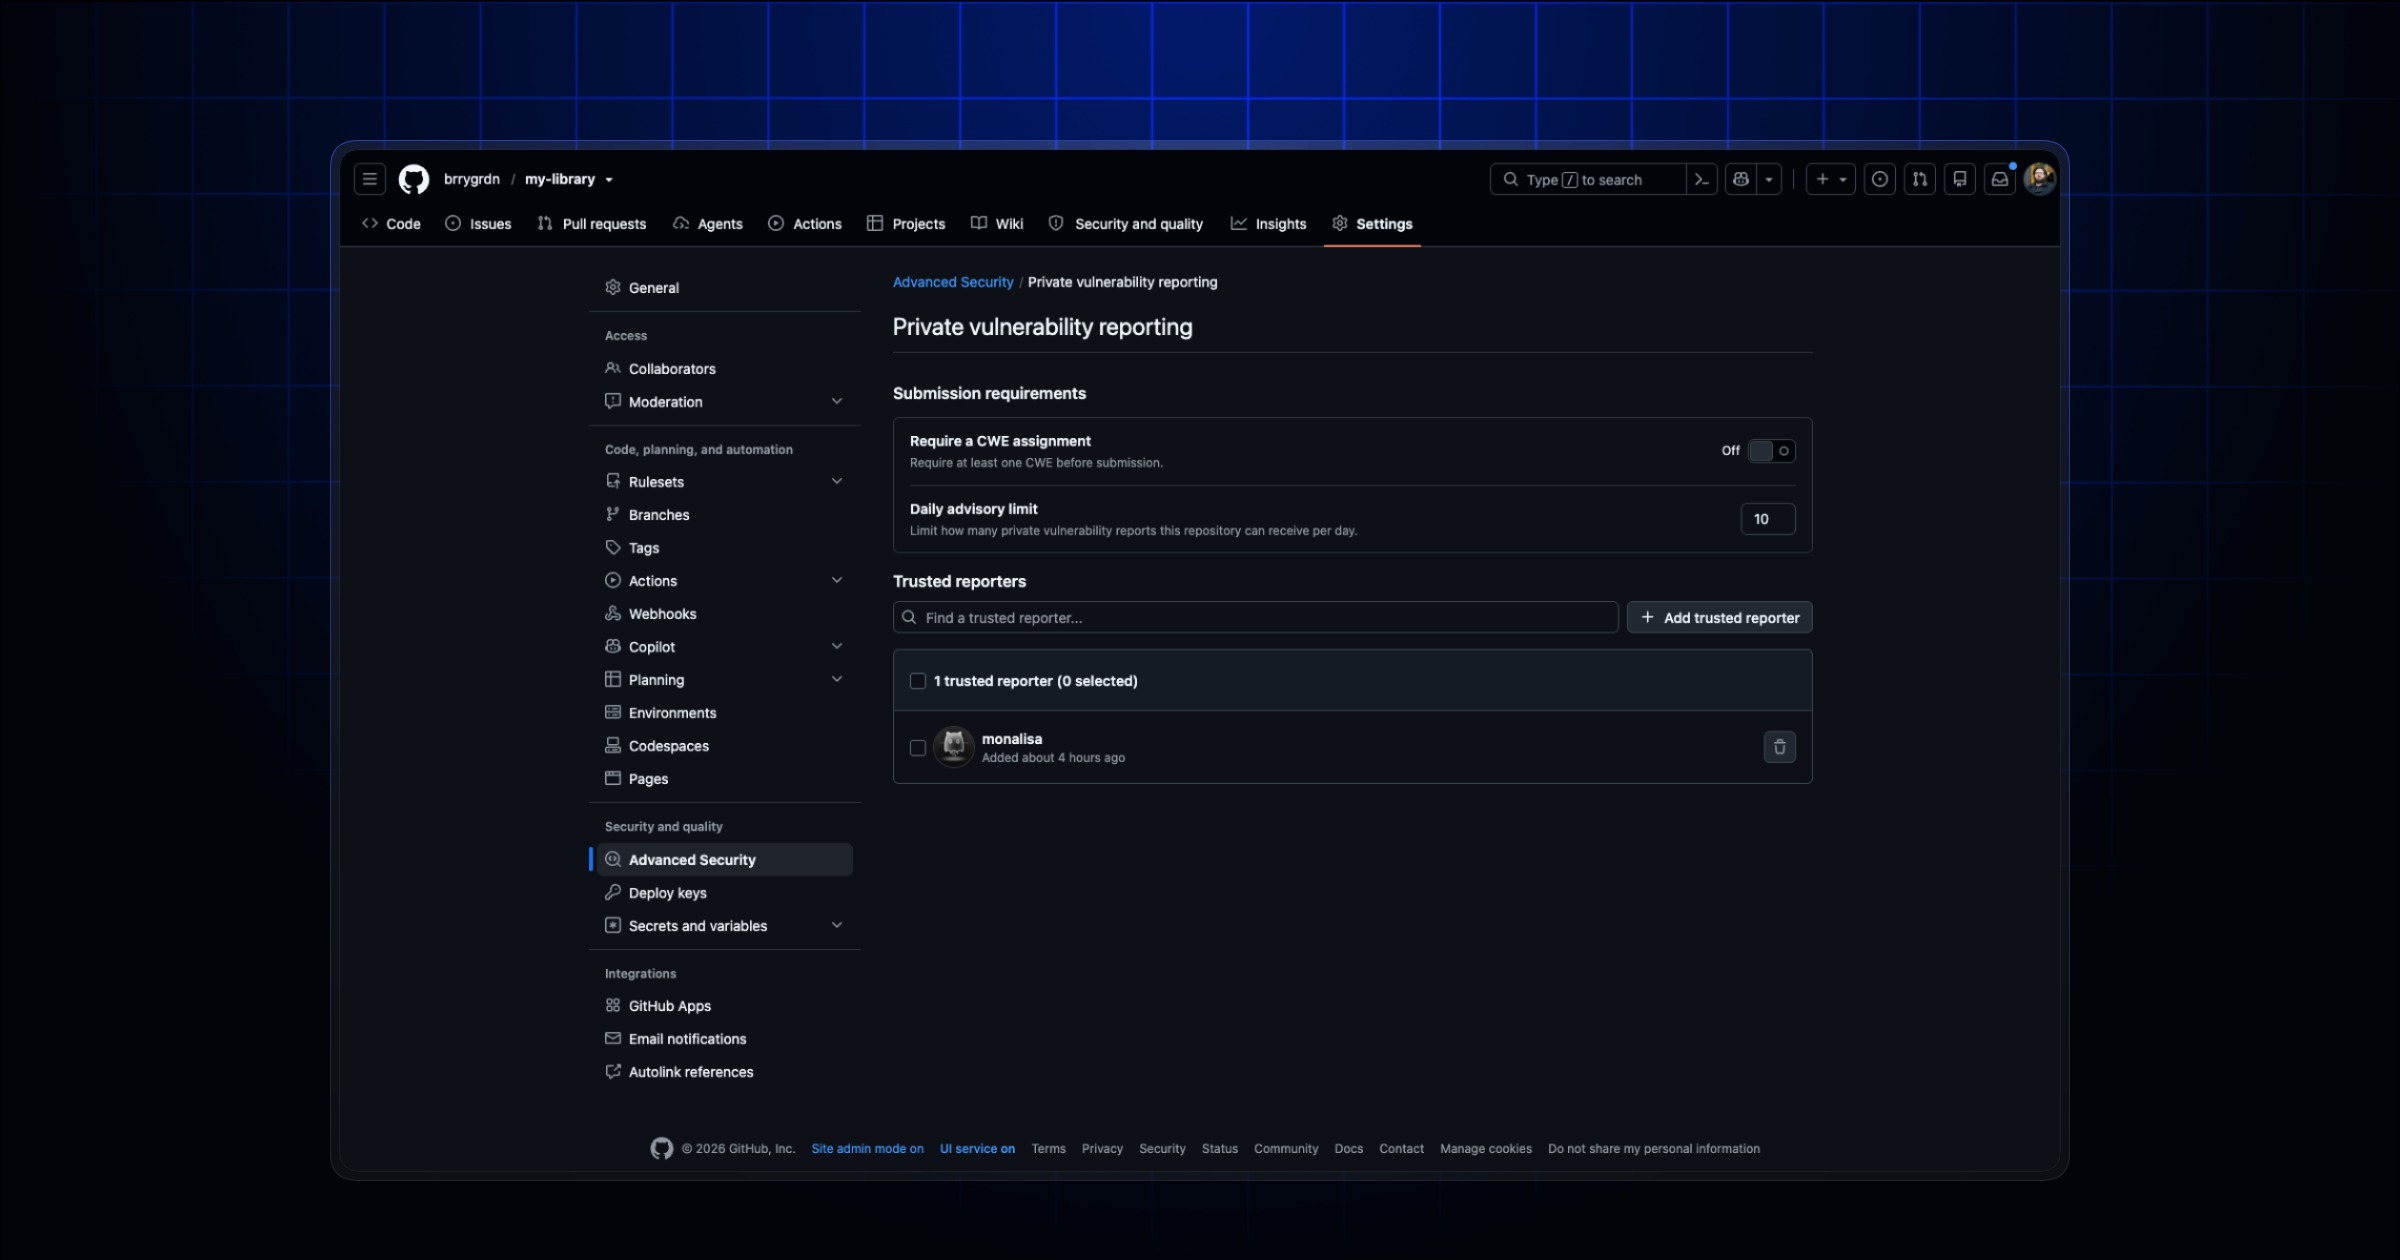
GitHub reports that maintainers are increasingly overwhelmed by low‑quality, automated vulnerability submissions, which can hide important findings. To address this, the platform now imposes a daily per‑user limit on the number of new private vulnerability reports an account can file, both for a specific repository and across GitHub as a whole, while leaving comments on existing advisories untouched. Users who exceed the cap receive a notice to retry later. Repository owners may define a custom overall daily limit for their project and can create an allow list of trusted researchers who are exempt from throttling. These settings are accessed via the repository’s Advanced Security section and are available for public repositories with private reporting enabled on all GitHub plans.